Requirements (SaaS)
This page describes the network architecture and connectivity requirements when using the meltcloud SaaS (https://app.meltcloud.io).
In this setup, Nest (which hosts the control planes and the Foundry) is hosted as SaaS in the Internet and only the workers run locally. Thus, only connectivity from the workers to the SaaS is required.
Architecture
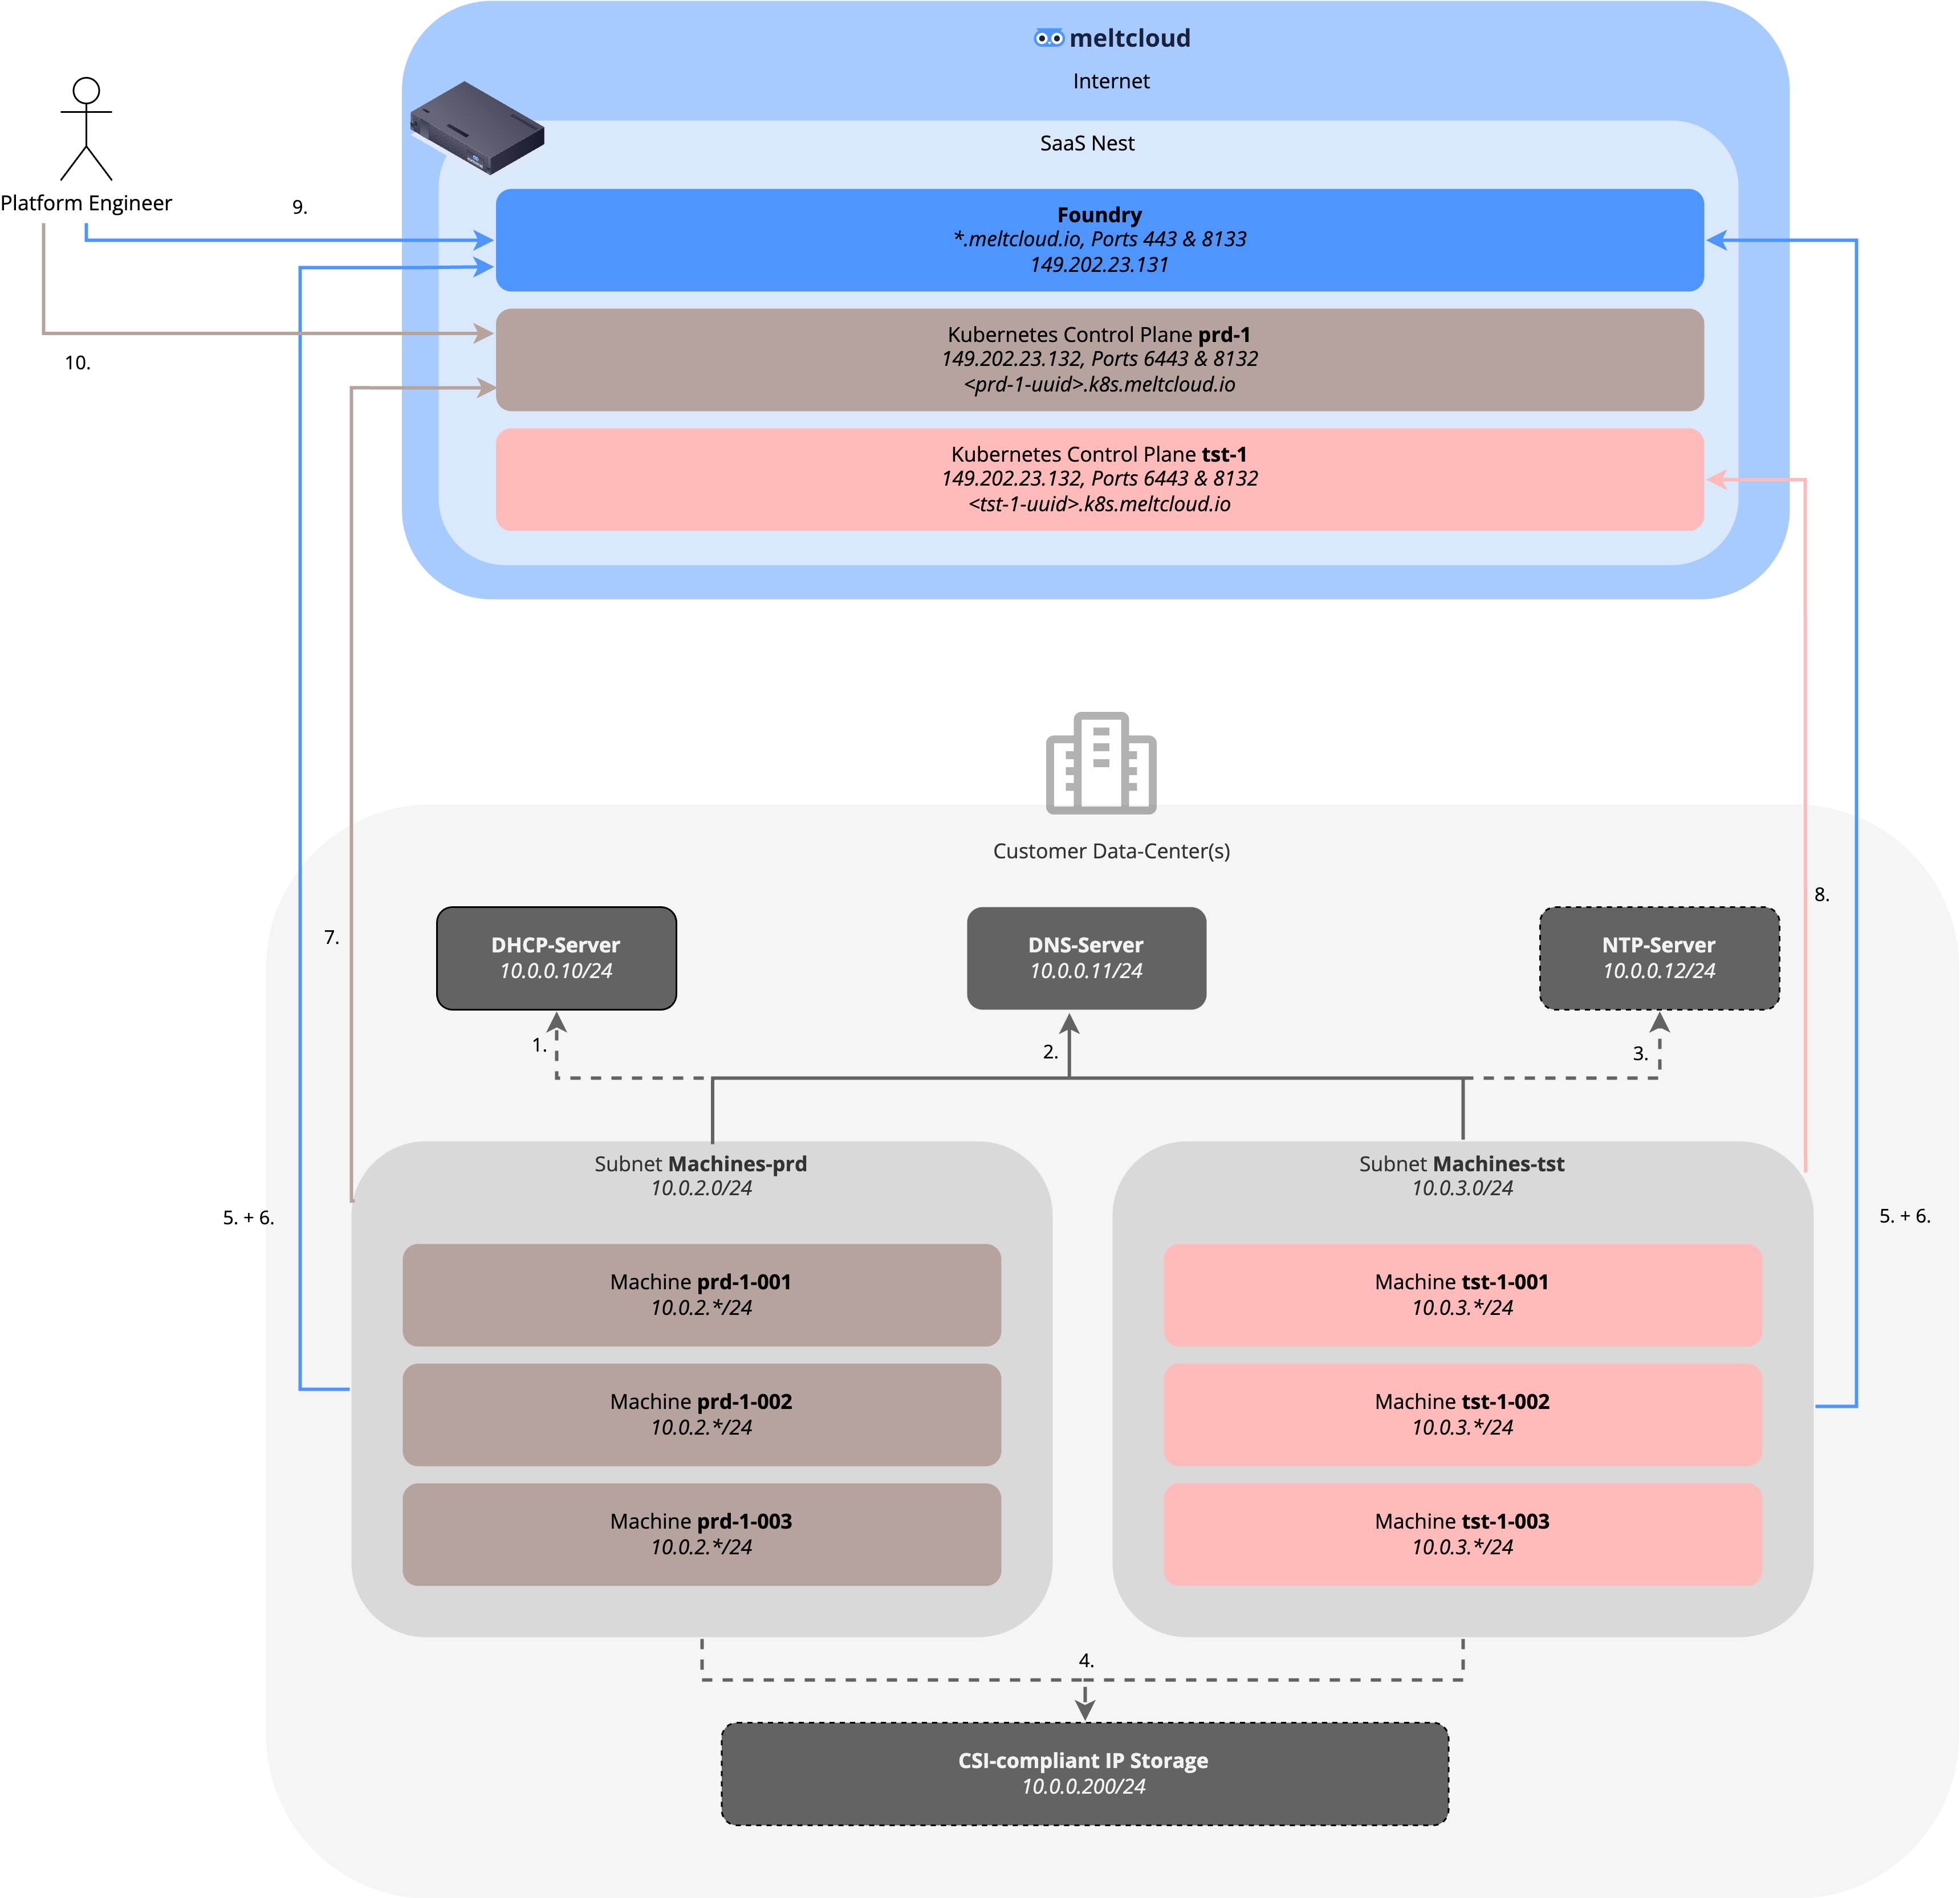
The following image depicts the involved components and their connectivity flows. To illustrate it with examples, we have chosen the 10.0.0.0/8 RFC1918 range as an example.
Customer-provided Services
As shown in the picture above, meltcloud requires the following services to be provided by the customer:
- DNS: to resolve all internal and external destinations
- NTP-Server, optional: to synchronize time of Machines. Strongly recommended to avoid issues with TLS client certificates. If none provided, Machines will fall back to
*.flatcar.pool.ntp.org. - DHCP-Server, optional: to provide IP addresses, routes, DNS & NTP servers for all Machines. Alternatively, you can use meltcloud's IPAM addressing mode. See Subnet Addressing for details.
- Egress Internet Connectivity: Connectivity to
*.meltcloud.io. There is currently no support for HTTP proxies when using the SaaS.
Port Matrix
The following table shows all required connectivity according to the image above:
| ID | Source | Destination | Ports/Protocols | Reason | Required | Comment |
|---|---|---|---|---|---|---|
| 1 | Subnets Machines-* (10.0.2-3.0/24) | DHCP-Server (10.0.0.10) | 67/udp (DHCP) | To retrieve IPs, routes, DNS & NTP server | No | Only with DHCP addressing. Not needed with IPAM |
| 2 | Subnets Machines-* (10.0.2-3.0/24) | DNS-Server (10.0.0.11) | 53/udp/tcp (DNS) | To resolve hostnames | Yes | |
| 3 | Subnets Machines-* (10.0.2-3.0/24) | NTP-Server (10.0.0.12) | 123/udp (NTP) | To synchronize time | No | If unset, falls back to *.flatcar.pool.ntp.org |
| 4 | Subnets Machines-* (10.0.2-3.0/24) | CSI-compliant IP Storage (10.0.0.200/24) | NFS, iSCSI, ... | For persistent volumes | No | Depends on vendor/technology |
| 5 | Subnets Machines-* (10.0.2-3.0/24) | Foundry, agent.meltcloud.io and pkg-pub.meltcloud.io (149.202.23.131) | 443/tcp (HTTPS) | Agent <> Foundry interaction, downloading of packages | Yes | Uses TLS Client Certificates |
| 6 | Subnets Machines-* (10.0.2-3.0/24) | Foundry, agent.meltcloud.io (149.202.23.131) | 8133/tcp (HTTPS) | Tunnelled TLS traffic for in-cluster Pod -> kube-apiserver traffic (as the SNI listener cannot be used for this traffic) | Yes | Same IP as ID 5, different port |
| 7 | Subnet Machines-prd (10.0.2.0/24) | Kubernetes control plane prd-1, <prd-1-uuid>.k8s.meltcloud.io (149.202.23.132) | 6443/tcp, 8132/tcp (HTTPS) | Kubelet -> kube-apiserver and konnectivity traffic | Yes | Uses TLS Client Certificates. Every Cluster uses these same ports and is told apart by its hostname (SNI) |
| 8 | Subnet Machines-tst (10.0.3.0/24) | Kubernetes control plane tst-1, <tst-1-uuid>.k8s.meltcloud.io (149.202.23.132) | 6443/tcp, 8132/tcp (HTTPS) | Kubelet -> kube-apiserver and konnectivity traffic | Yes | Uses TLS Client Certificates. Every Cluster uses these same ports and is told apart by its hostname (SNI) |
| 9 | platform engineer | Foundry, app.meltcloud.io (149.202.23.131) | 443/tcp (HTTPS) | web (including Websockets) or API interaction | Yes | |
| 10 | platform engineer | Kubernetes control plane prd-1, <prd-1-uuid>.k8s.meltcloud.io (149.202.23.132) | 6443/tcp (HTTPS) | kubectl interaction | No | The admin kubeconfig uses TLS Client Certificates, the user kubeconfig authenticates via OIDC |